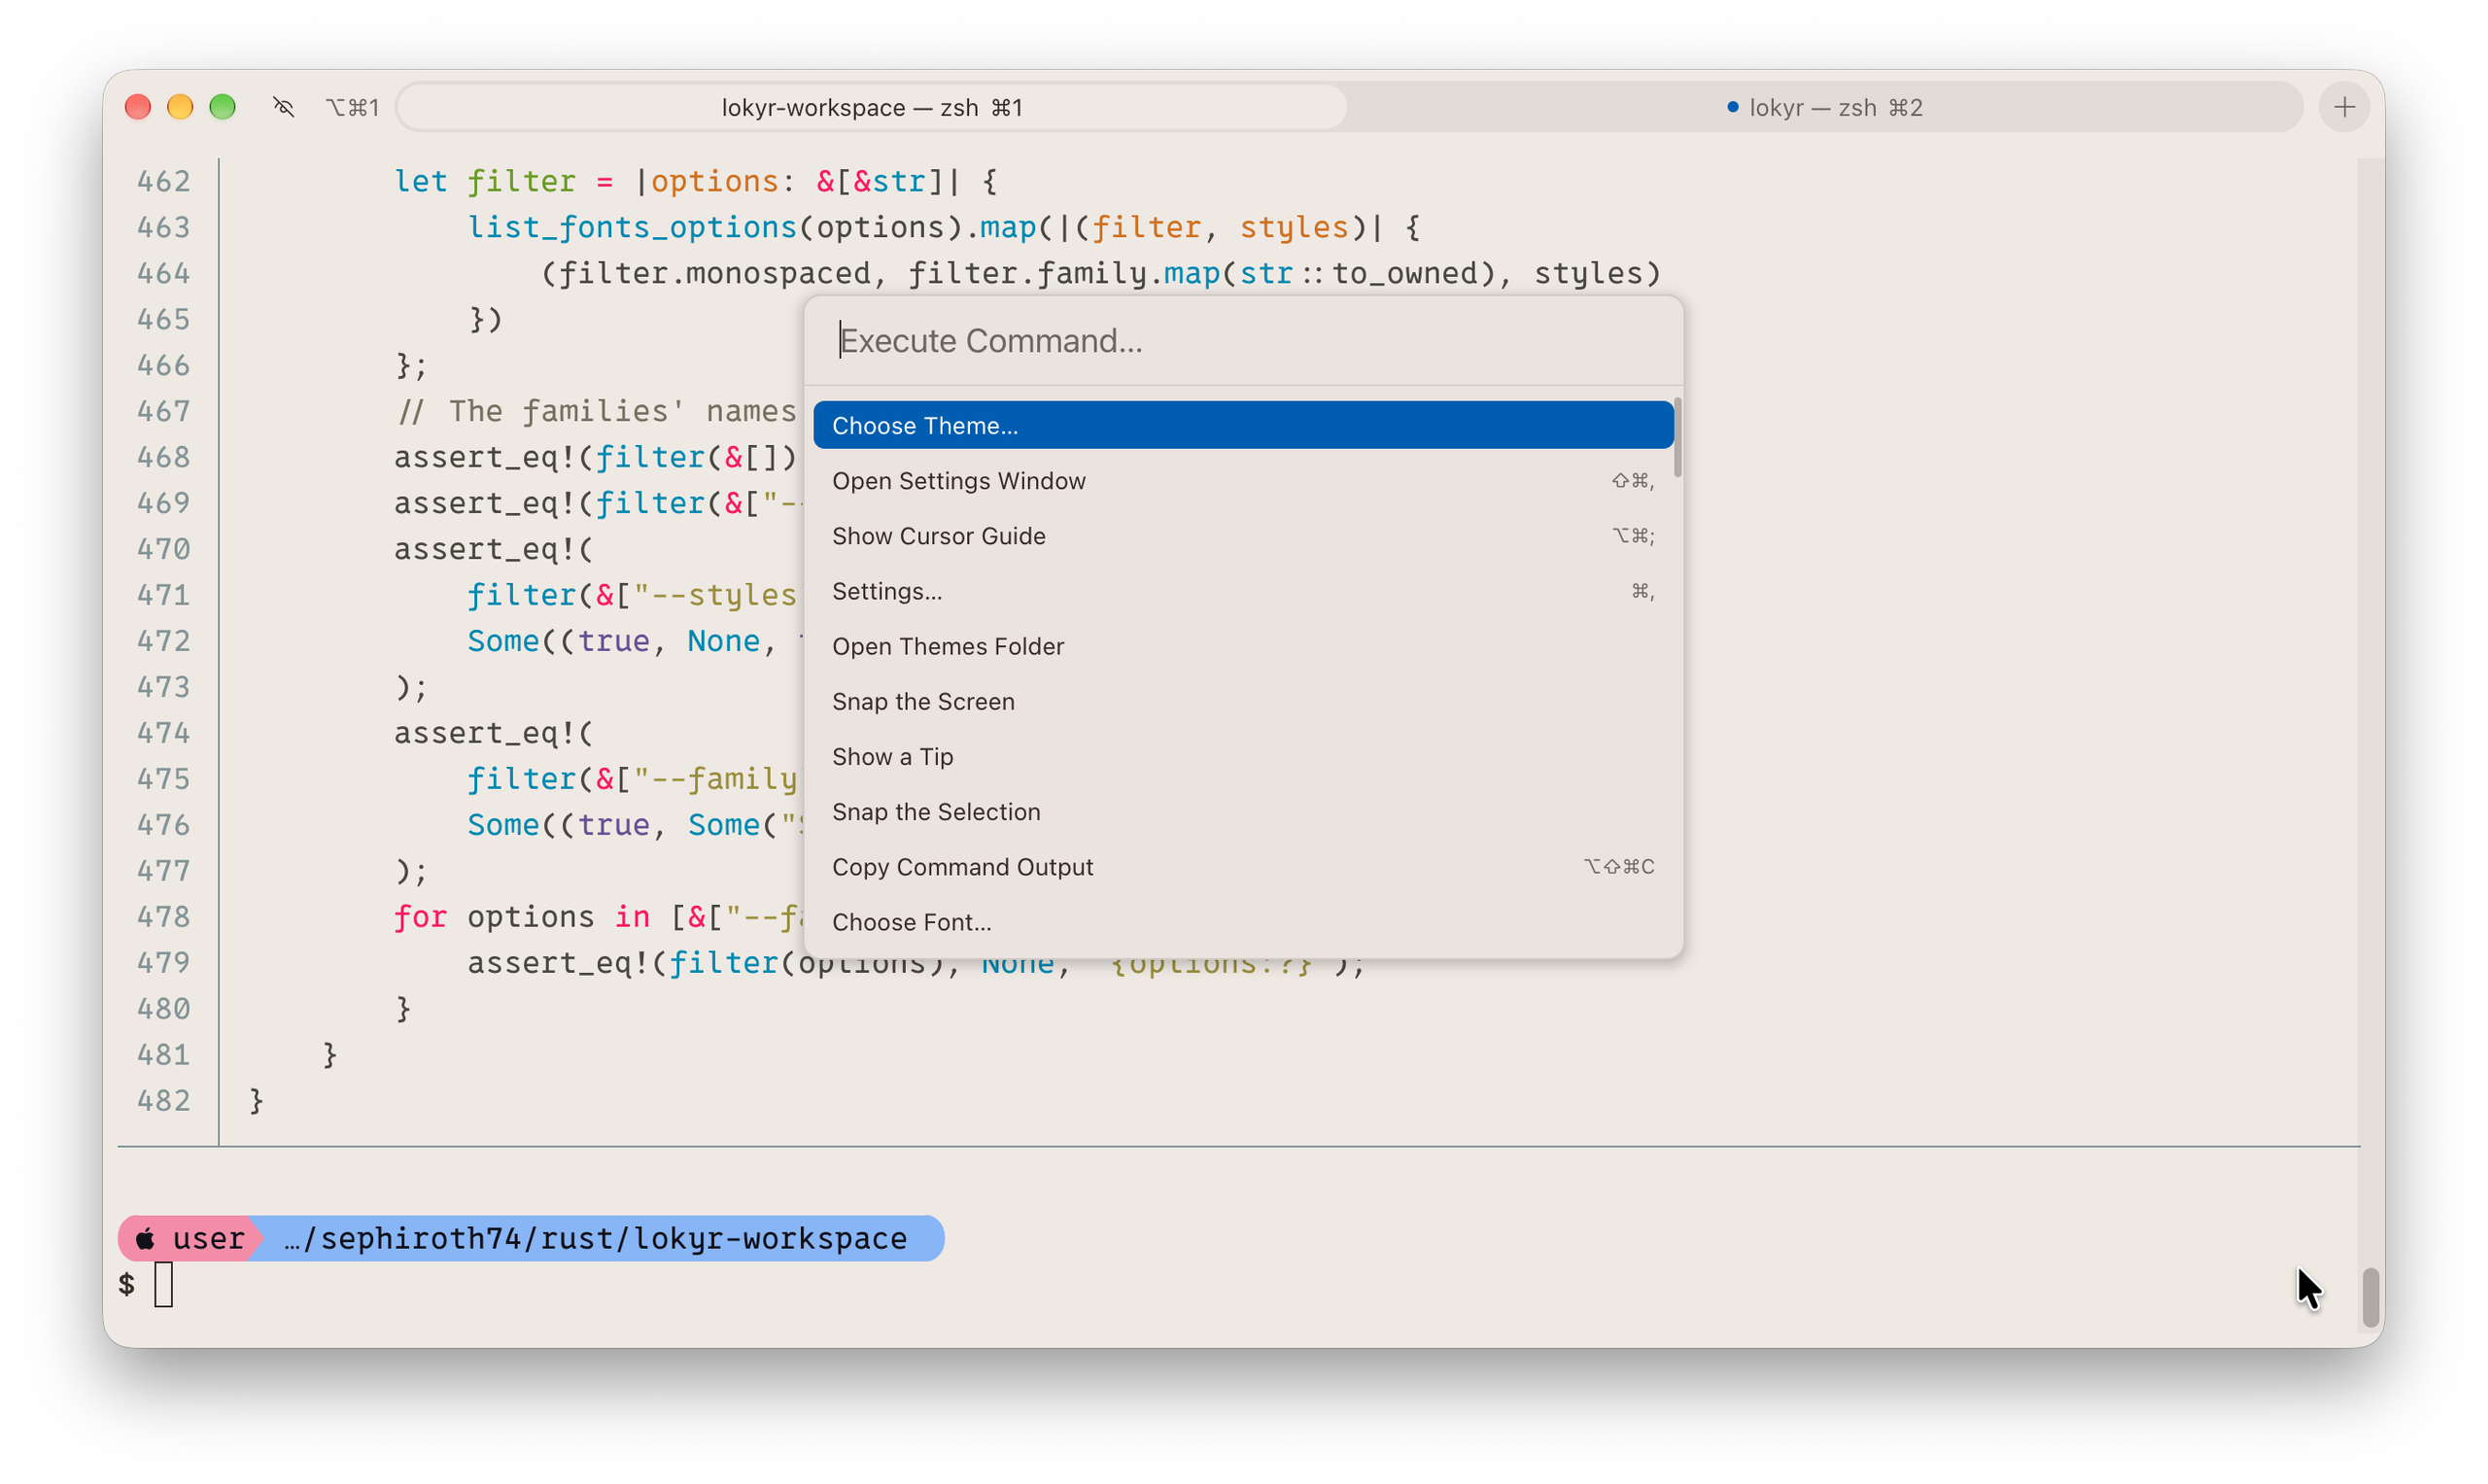
I’d like to introduce Lokyr, a terminal emulator for macOS I started a little more than a month ago.
I spend most of my day in a terminal, and over the years I’ve tried practically all of them: Terminal.app, iTerm2, Alacritty, kitty, WezTerm, Ghostty, and probably a few more I don’t even remember. Every one of them had something I liked, but none of them had everything I wanted, at least not all together.. so I always ended up going back and forth between two or three of them.
So I thought: why not make my own? Writing a terminal emulator from scratch is not exactly a small project (and honestly I know a little about it), so I decided to make it an experiment in vibe coding too: I described what I wanted, an AI agent wrote the code, and my job was to use it every day, test it, measure it and ask for changes until it worked the way I wanted.
The result is Lokyr.
What it is
Lokyr is written in Rust and it’s native on macOS: an AppKit window, Metal for the rendering, CoreText for the fonts.
The idea behind it is a small core, the terminal itself (the screen, the input, the rendering), with everything else as a plugin. The tab bar, the splits, the search and the command palette are all plugins, built on the same API that third party plugins get, so if you don’t need one of them you can just turn it off.
Third party plugins are written in Luau and run in a sandbox: each plugin has to declare what it wants to access (the screen, the clipboard, files, the network) and Lokyr asks you before the first use. They are installed with Sleip, Lokyr’s own package manager.
Some of the other things I wanted, which are already there:
tabs at the top, at the bottom or on a side, and split panes
shell integration for zsh, bash and fish: jump between prompts, the outcome of each command, a notification when a long command ends
a quick terminal that slides in from an edge of the screen with a global shortcut
tabs that show what the AI agent inside them is doing (Claude Code, Codex, Gemini CLI): working, waiting for you, or done
themes, and since version 1.2.0 a theme editor in the settings window
a TOML config file, applied as soon as you save it
Performance was one of the goals since the beginning, so every change is measured against the previous builds and against six other terminals. Lokyr does better on some measures and not on others: all the numbers are in the repository.
Install
Lokyr requires macOS 26 or later on Apple Silicon. You can download the DMG from the website, or install it with Homebrew:
brewinstall--casksephiroth74/tap/lokyr
After that, Lokyr updates itself.
It’s open source (MIT license) and it’s still a work in progress, so there’s a lot more on my list.
I am writing this guide for my future self, for the next time he inadvertently destroys the Raspberry Pi’s SD card.! This is a simple deep-dive on turning a Raspberry Pi 5 into a secure home server. In this guide, we will transform a raw micro-SD card into a self-hosted infrastructure featuring network-wide ad-blocking (AdGuard Home), private VPN access (WireGuard), reverse proxy routing (Nginx Proxy Manager), root-level file management (Filebrowser), centralized Docker administration (Portainer), automated encrypted cloud backups (Kopia + Rclone), and a clean unified dashboard (Homepage).
Before starting, ensure you have the following hardware:
Single Board Computer: Raspberry Pi 5 (8GB RAM recommended).
Storage: High-speed A2-rated MicroSD card (64GB+) or NVMe M.2 SSD with PCIe HAT.
Power Supply: Official 27W USB-C Power Supply.
Network Connection: Ethernet cable connected directly to your primary router.
2. MicroSD Preparation with Raspberry Pi Imager
We will flash Raspberry Pi OS (64-bit) using the official Raspberry Pi Imager to pre-configure SSH and user credentials headlessly.
Download & Install: Download Raspberry Pi Imager from the official website.
Select Device & OS:
Device: Raspberry Pi 5
OS: Raspberry Pi OS (64-bit) (Debian Bookworm)
Storage: Select your inserted MicroSD card.
Configure OS Customization Settings:
Click EDIT SETTINGS:
General Tab:
Set hostname: Raspberry-PI5
Set username: kenshiro
Set password: (Enter a secure password)
Configure Wireless LAN (optional, Ethernet preferred).
Set Locale Settings (Time zone and Keyboard layout).
Services Tab:
Check Enable SSH → Select Use password authentication.
Click SAVE and proceed to flash the MicroSD card.
3. Initial System Setup & Network Discovery
Insert the MicroSD card into your Raspberry Pi 5, attach the Ethernet cable, and power it on.
Step 3.1: Locating Your Raspberry Pi’s Local IP Address
Before establishing the first SSH connection, locate the local IPv4 address assigned to your Raspberry Pi by your router’s DHCP server:
Method 1: Router Admin Interface (Recommended): Log in to your router’s web interface (e.g., http://192.168.1.1). Navigate to Connected Devices or DHCP Client List and locate the device named Raspberry-PI5.
Method 2: Hostname Resolution (mDNS): On macOS, Linux, or Windows (with Bonjour/mDNS enabled), open your terminal and ping the hostname directly:
pingRaspberry-PI5.local
Method 3: Network Scanning: Use a mobile network scanner app (e.g., Fing) or run a command-line utility on your local network:
arp-a|grep-i"Raspberry"
Step 3.2: Connect via SSH
Once you have retrieved the IP address (e.g., 192.168.1.118), connect via SSH using the username kenshiro:
sshkenshiro@192.168.1.118
Or using mDNS hostname
sshkenshiro@Raspberry-PI5.local
Step 3.3: System Update & Directory Workspace
Perform a full upgrade of Debian packages and establish a clean /opt workspace structure:
Global Unicast Address (2a02:... or 2001:...): Public IPv6 assigned dynamically by your ISP.
Link-Local Address (fe80::...): Static local IPv6 address. Recommended for router setup because it never changes, even if your ISP updates your public IPv6 prefix.
Quick alternative: Run hostname -I to view all assigned IPs simultaneously.
Method 2: Via AdGuard Home Web UI:
Open http://192.168.1.118:8080, navigate to Setup Guide, and locate the detected IPv4 and IPv6 addresses.
Router Configuration Steps
Static IP Reservation:
Assign a fixed IPv4 address to your Raspberry Pi 5 MAC address (192.168.1.118).
Router DNS Delegation (IPv4 & IPv6):
Primary IPv4 DNS: Set to 192.168.1.118.
Primary IPv6 DNS (DHCPv6): Set “DNS Server IPv6 notified through DHCPv6” to your Raspberry Pi’s Link-Local address (fe80::8aa2:9efe:fe96:f29e).
Why IPv6 DNS is critical: Notifying AdGuard’s IPv6 address ensures all network devices resolve DNS via AdGuard regardless of connection protocol.
Port Forwarding (Remote Access via WireGuard):
WireGuard VPN: Forward External UDP Port 51820 → 192.168.1.118:51820.
Ports 80 & 443 (HTTP/HTTPS): Keep ports 80 and 443 closed to the Internet. Following a “VPN-First” security architecture, Nginx Proxy Manager handles reverse proxying internally. Remote access to web services is securely tunneled through WireGuard, keeping your server hidden from public port scanners.
To grant Filebrowser full access to host system directories (/opt, /etc, /home), run the container with root permissions (user: "0:0"), map root / to /srv, and explicitly specify the listening address --address 0.0.0.0.
10. Local Domain Routing (AdGuard Home & Nginx Proxy Manager Integration)
To access your containerized services using friendly custom domain names (such as files.home or portainer.home) instead of remembering IP addresses and port numbers (192.168.1.118:8082), AdGuard Home and Nginx Proxy Manager work in tandem:
AdGuard Home (DNS Level): Intercepts local domain requests (e.g., files.home) and resolves them to the Raspberry Pi’s local IP address (192.168.1.118).
Nginx Proxy Manager (Application Level): Listens on HTTP port 80, inspects the incoming host header (files.home), and reverse-proxies the traffic to the designated container’s port (e.g., 8082).
Today I’d like to introduce an extension I’ve created for Adobe Photoshop: Opacity Editor.
I like to take pictures, ok, I’m definitely not a professional photographer, but I still like to try to be one 🙂
In particular I like to take pictures at night, I like to take pictures of moving clouds, stars.. etc. And then I like to stack all the photos into a single document. The problem is that most of the times this Photoshop document has hundreds, if not thousands, of layers (and we’re talking about 40MP images) and, despite the fact that photoshop can barely survive after I’ve added all those layers to the document, the real problem comes after that.. In order to create a nice stacking effect it’s not just a matter of changing the blending mode of the different layers, but also to change their opacity.
Unfortunately Photoshop doesn’t have an option to manage the opacity of multiple layers at the same time, like, for instance, from 0 to 100 of all the selected layers.. or even more advanced options.
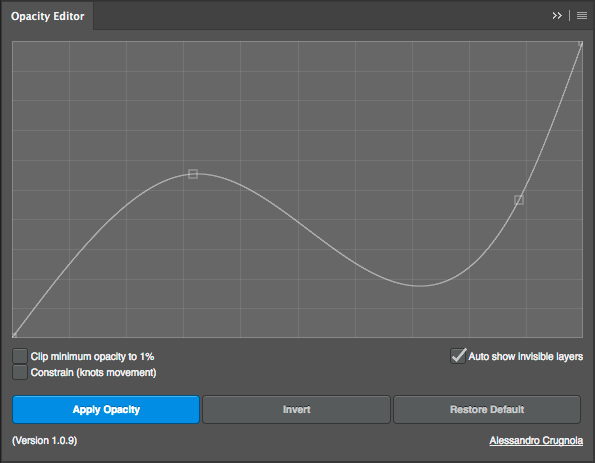
That’s why I’ve decided to make an extension (available here) for this. This is it’s pretty easy interface:
So basically what it does is: you select a bunch of layers in your document, then you create the bezier curve. Once you click on “Apply Opacity” the opacity of every selected layer will follow the designed curve value. Let’s make it easier. If you design a curve like this:
the first selected layer will have an opacity of 0 (completely invisible), while the last layer will have 100 as opacity. (If you’ve selected 100 layers, then the second one will have an opacity value of 1, the third of 2 and so on..)
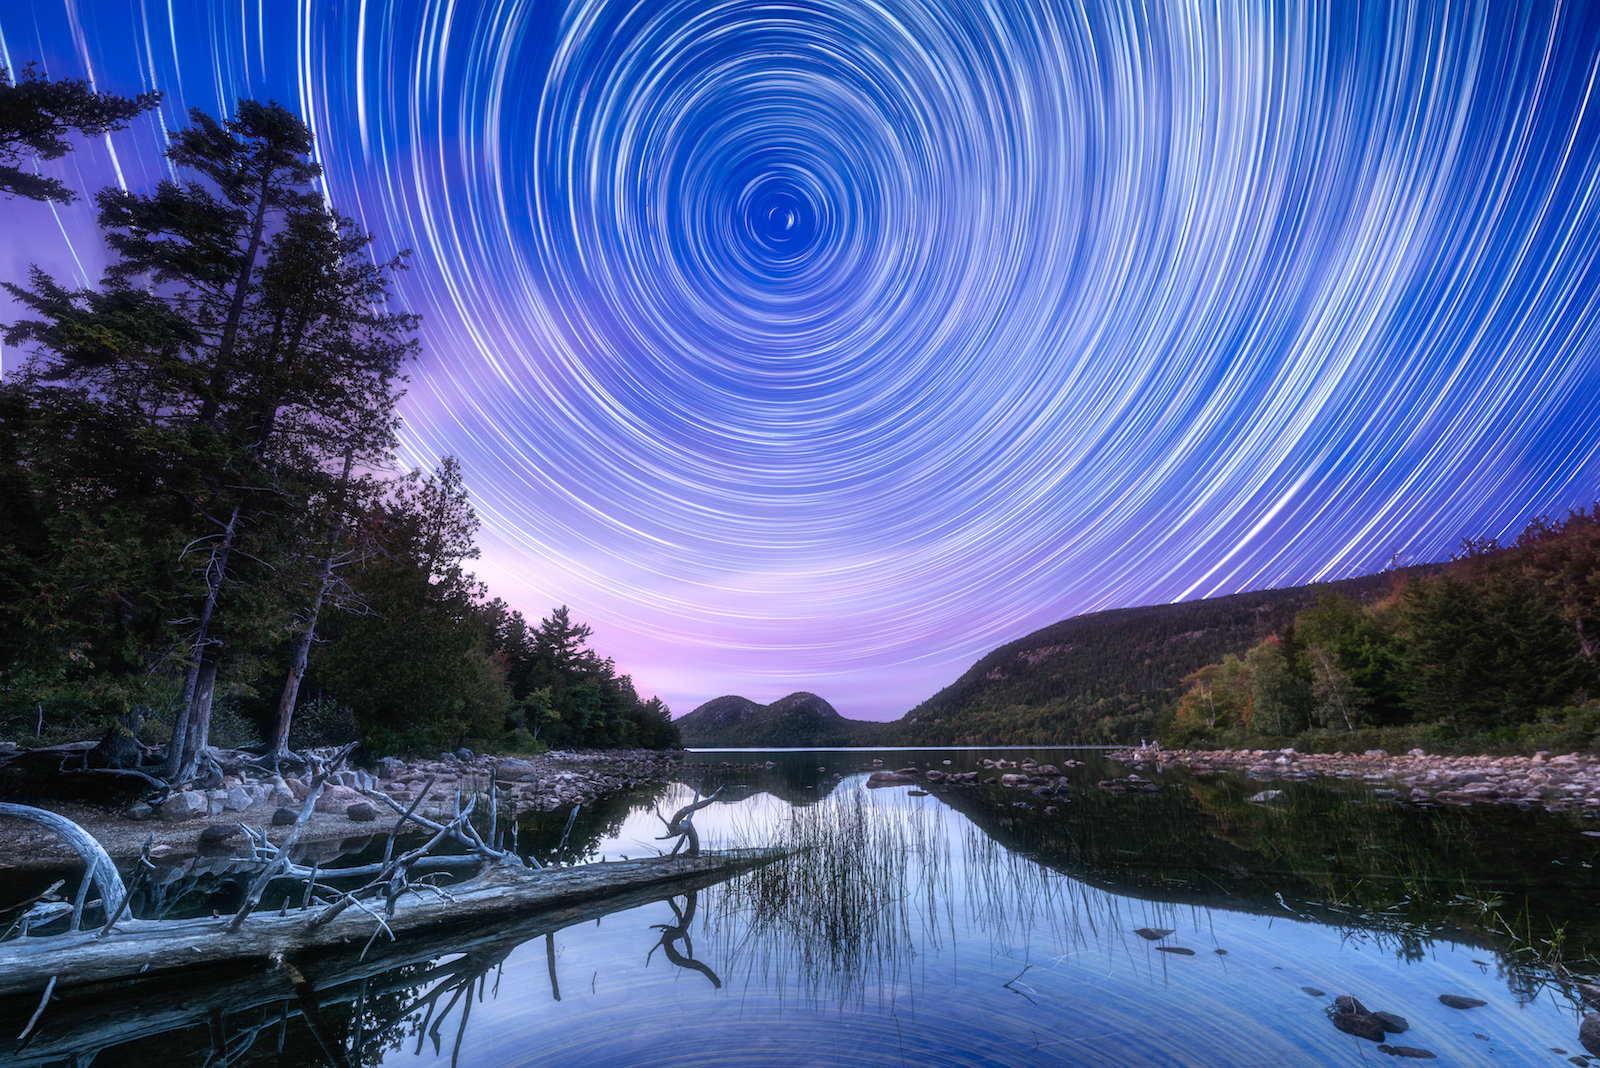
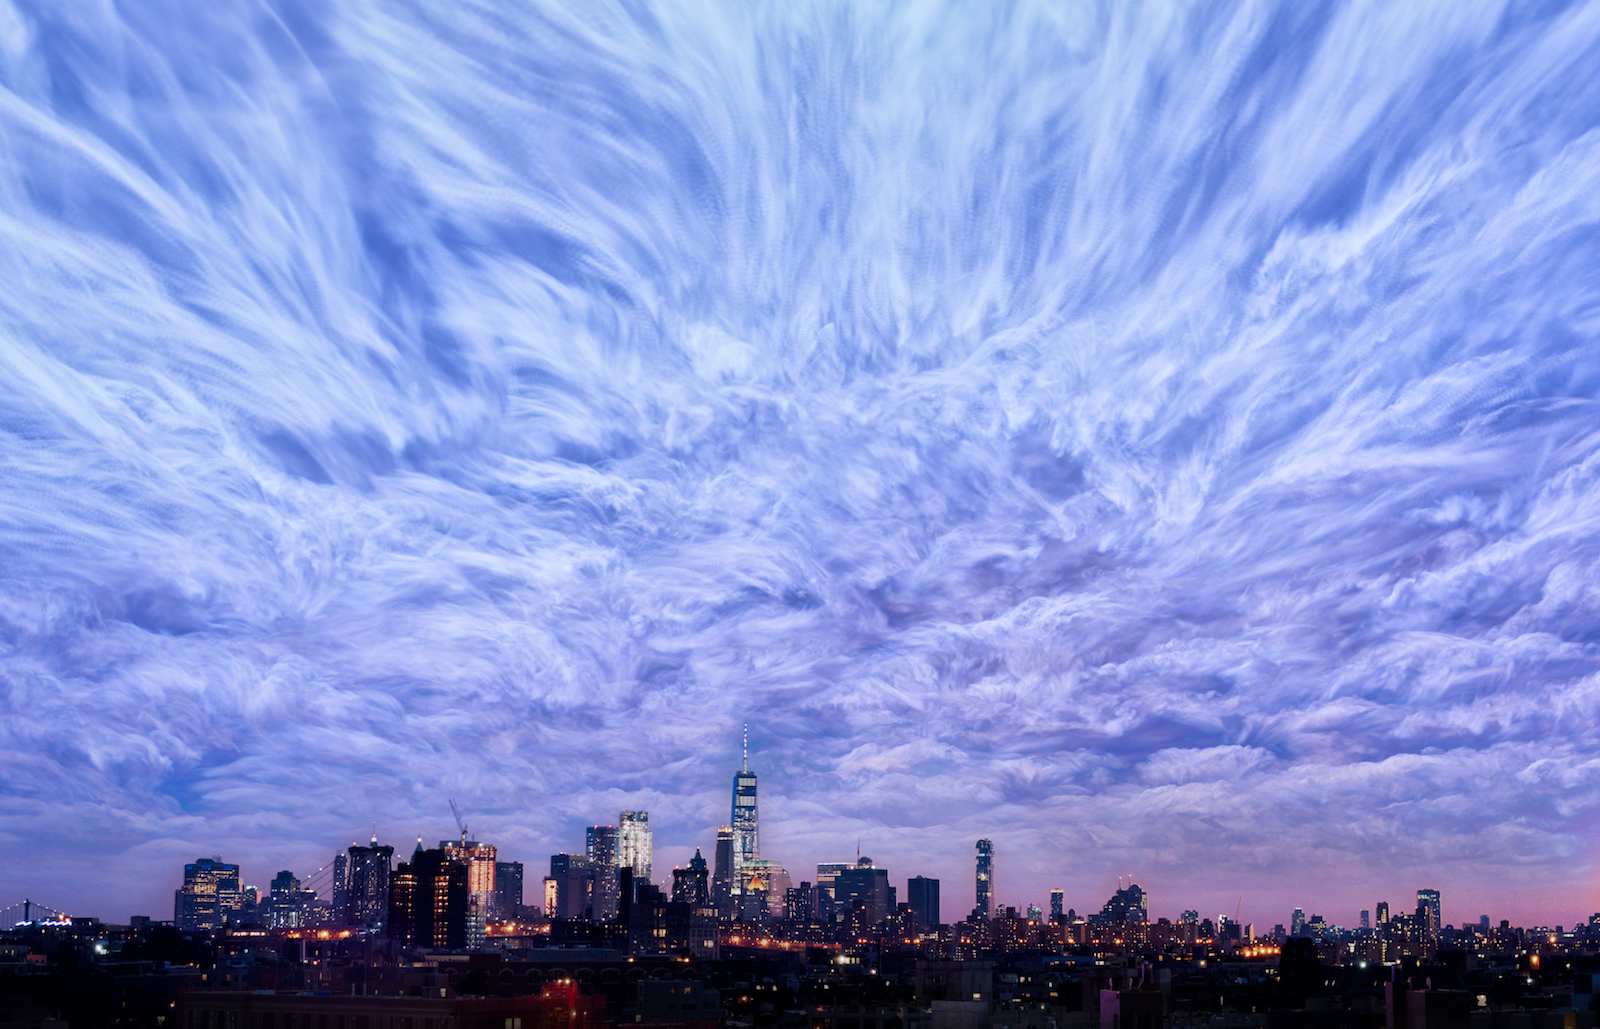
These 2 images, for instance, have been created using this extension:
1200~ pics
The second one is the result of 1200 layers stacked together and without that extension I would probably still working on it!
I’m an Android developer (at Aviary) and a New Yorker since late 2010. I’ve been also an actionscript and python developer for more than 10 years.
I hear this every day. Your New York based company is desperately looking for an Android developer, and it’s damn hard to find one.
And you know what? This is your fault. I mean you, tech startup. Yes, you.
Almost all the startups I know here in NYC have launched their core product for iOS first (most of the PMs I’ve spoken with have said that was because of lack of people or time). And then, maybe, if there’s time… they start to realize they need to have an Android version of their app. But by this point the job is not to “create” something, it’s just a “porting” job. Which, for obvious reasons, is a much less attractive job for developers, just as it would be for a PM or a designer. Continue reading →
I’ve just created this simple Android library, inspired from the recent changes to the Google+ app, which introduced a floating action item to the bottom. In G+ the action item appears and disappears based on the page scrolling.
In the same way I’ve created this library, with some more customization options, like the gravity and direction of the floating menu items.
Here’s a video of a sample implementation:
Source code and documentation can be find on the github project page:
If you ever worked with native shared libraries in Android you’ve probably already faced the “java.lang.UnsatisfiedLinkError” java exception which randomly seems to happen on certain devices ( actually it’s happening on xperia phones mostly, based on my reports ).
There are a bunch of bug reports in the android project like this: https://code.google.com/p/android/issues/detail?id=35962 or this https://code.google.com/p/android/issues/detail?id=64111.
The problem is that Google basically marked all of them as “resolved”, even if developers are still complaining about it.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.